

Latest 300-410 Pass Guaranteed Exam Dumps with Accurate & Updated Questions
300-410 Exam Brain Dumps - Study Notes and Theory
NEW QUESTION # 370
Refer to the exhibit.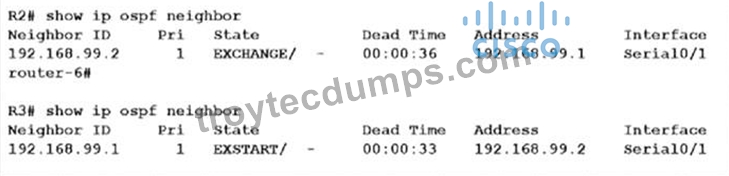
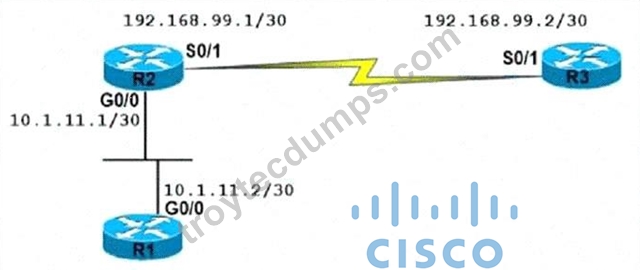
An OSPF neighbor relationship between R2 and R3 is showing stuck in EXCHANGE/EXSTART state. The neighbor is established between R1 and R2. The network engineer can ping from R2 to R3 and vice versa, but the neighbor is still down. Which action resolves the issue?
- A. Restore the Layer 2/Layer 3 conectivity issue in the ISP network.
- B. Match MTU on both router interfaces or ignore MTU.
- C. Enable OSPF on the interface, which is required.
- D. Administrative "shut then no shut" both router interfaces.
Answer: B
Explanation:
After two OSPF neighboring routers establish bi-directional communication and complete DR/BDR election (on multi-access networks), the routers transition to the exstart state. In this state, the neighboring routers establish a master/slave relationship and determine the initial database descriptor (DBD) sequence number to use while exchanging DBD packets.
Neighbors Stuck in Exstart/Exchange State
The problem occurs most frequently when attempting to run OSPF between a Cisco router and another vendor's router. The problem occurs when the maximum transmission unit (MTU) settings for neighboring router interfaces don't match. If the router with the higher MTU sends a packet larger that the MTU set on the neighboring router, the neighboring router ignores the packet.
NEW QUESTION # 371
Refer to the exhibit.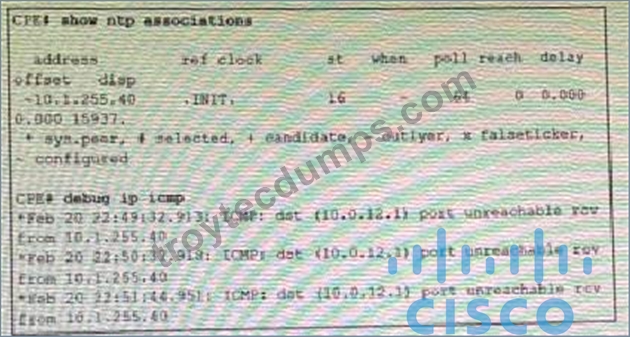
An administrator is troubleshooting a time synchronization problem for the router time to another Cisco IOS XE-based device that has recently undergone hardening. Which action resolves the issue?
- A. Allow NTP in the ingress ACL on 10.1.225.40 by permitting UDP destined to port 123.
- B. NTP service is disabled and must be enabled on 10.1.225.40.
- C. Ensure that he CPE router has a valid route to 10.1.255. 40 for NTP and rectify if not reachable.
- D. Allow NTP in the ingress ACL on 10.1.255.40 by permitting TCP destined to port 123.
Answer: B
NEW QUESTION # 372
Drag and drop the addresses from the left onto the correct IPv6 filter purposes on the right.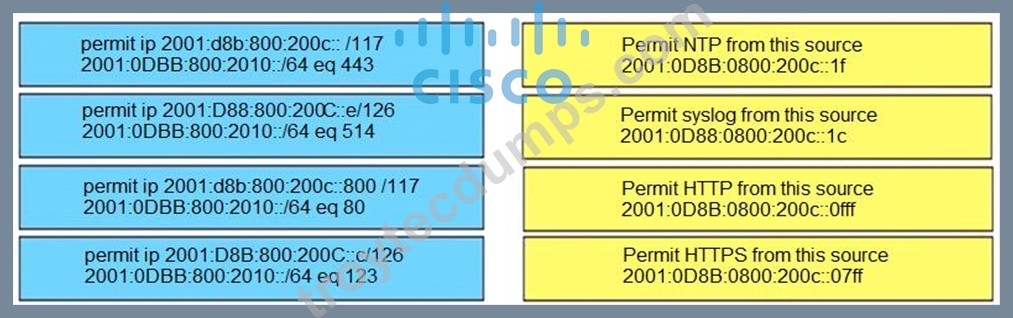
Answer:
Explanation: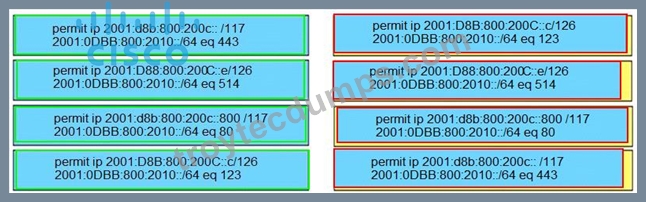
NEW QUESTION # 373
Refer to the exhibit. Which command must be configured to make VRF CCNP work?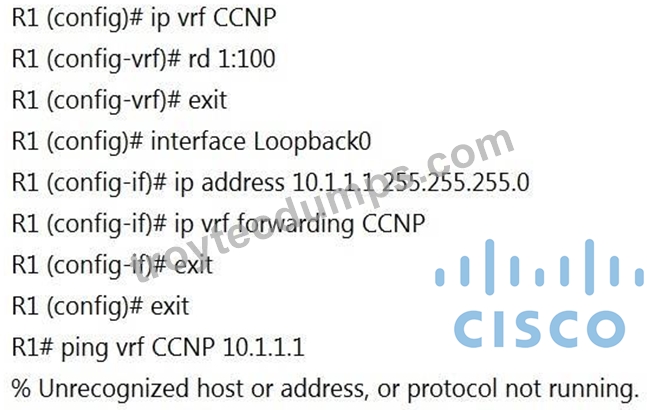
- A. interface Loopback0
vrf forwarding CCNP - B. interface Loopback0
ip address 10.1.1.1 255.255.255.0
ip vrf forwarding CCNP - C. interface Loopback0
ip address 10.1.1.1 255.255.255.0
vrf forwarding CCNP - D. interface Loopback0
ip address 10.1.1.1 255.255.255.0
Answer: D
Explanation:
It's the feature of MPLS VPN, it will create separate routing table other than global routing table and same will be referred only by interfaces who are in same VRF instance. This is why interface ip needs to be removed from global routing table. Interfaces in VRF will not be referred to global routing table under normal configuration.
NEW QUESTION # 374
Refer to the exhibit.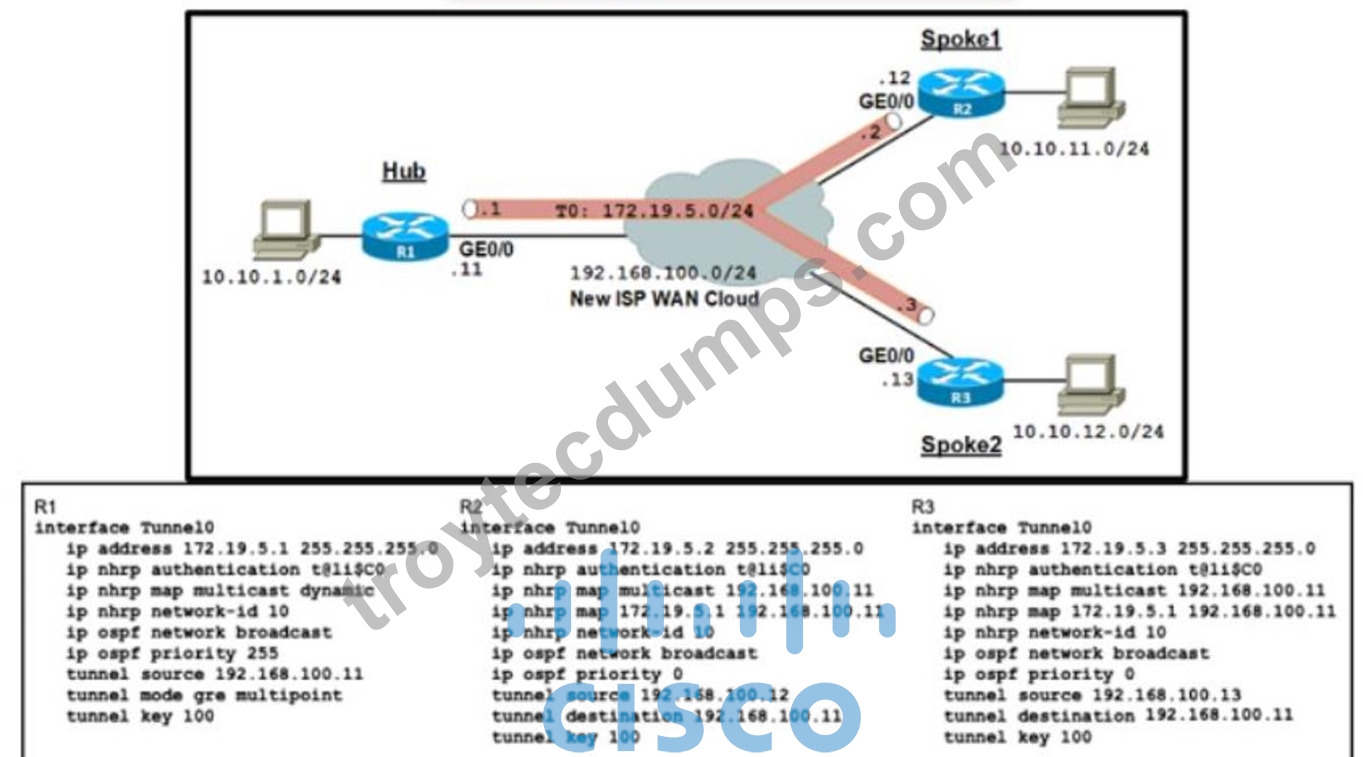
Refer to the exhibit. An organization is installing a new L3 MPLS link to establish DM VPN Phase 2 tunnels between the hub and two spoke routers Which additional configuration should the engineer implement on each device to achieve optimal routing between the spokes?
- A.

- B.
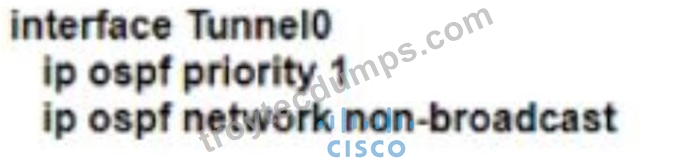
- C.
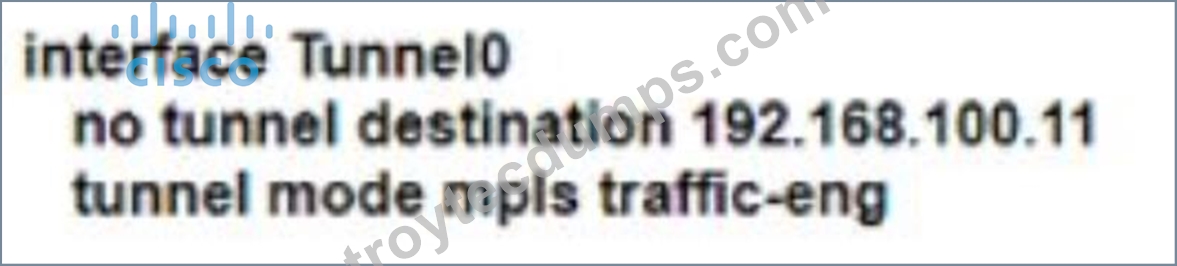
- D.
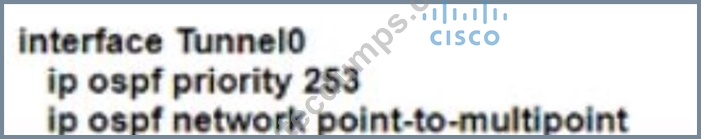
Answer: A
NEW QUESTION # 375
In which two ways does the IPv6 First-Hop Security Binding Table operate? (Choose two.)
- A. by IPv6 routing protocols to securely build neighborships without the need of authentication
- B. by various IPv6 guard features to validate the data link layer address
- C. by IPv6 HSRP to make sure neighbors are authenticated before being used as gateways
- D. by storing hashed keys for IPsec tunnels for the built-in IPsec features
- E. by the recovery mechanism to recover the binding table in the event of a device reboot
Answer: B,E
Explanation:
Overview of the IPv6 First-Hop Security Binding Table
A database table of IPv6 neighbors connected to the device is created from information sources such as NDP snooping. This database, or binding table, is used by variousIPv6 guard features to validate the link-layer address (LLA), the IPv4 or IPv6 address, and the prefix binding of the neighbors to prevent spoofing and redirect attacks.
IPv6 First-Hop Security Binding Table Recovery MechanismThe IPv6 first-hop security binding table recovery mechanism enables the binding table to recover in the event of a device reboot.
Reference:
https://www.cisco.com/c/en/us/td/docs/ios-xml/ios/ipv6_fhsec/configuration/15-s/ip6-fhs-bind-table.html
NEW QUESTION # 376
The network administrator configured R1 to authenticate Telnet connections based on Cisco ISE using TACACS+. ISE has been configured with an IP address of 192.168.1.5 and with a network device pointing toward R1(192.168.1.1) with a shared secret password of Cisco123.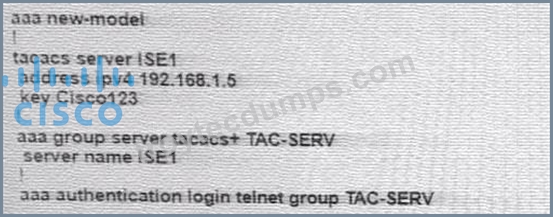
The administrator cannot authenticate to R1 based on ISE. Which configuration fixes the issue?
- A. line vty 0 4login authentication TAC-SERV
- B. line vty 0 4login authentication telnet
- C. ip tacacs-server host 192.168.1.5 key Cisco123
- D. tacacs-server host 192.168.1.5 key Cisco123
Answer: B
Explanation:
The last command "aaa authentication login telnet group TAC-SERV" created the method list name telnet so we need to assign it to line vty.
Reference: https://www.cisco.com/c/en/us/support/docs/security/identity-services-engine/200208- Configure-ISE-2-0-IOS-TACACS-Authentic.html
NEW QUESTION # 377 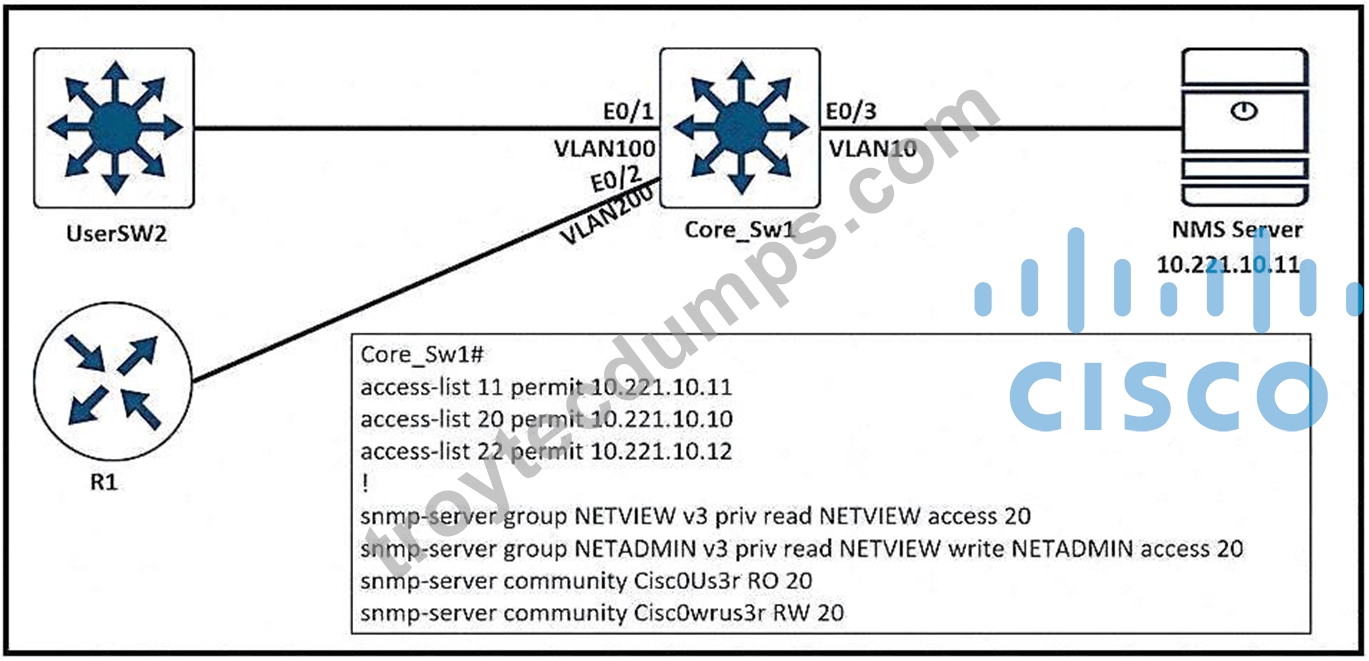
- A. access-list 20 permit 10.221.10.12
- B. snmp-server group NETVIEW v2c priv read NETVIEW access 20
- C. access-list 20 permit 10.221.10.11
- D. snmp-server group NETADMIN v3 priv read NETVIEW write NETADMIN access 22
Answer: C
NEW QUESTION # 378
An engineer configured a leak-map command to summarize EIGRP routes and advertise specifically loopback
0 with an IP of 10.1.1.1.255.255.255.252 along with the summary route. After finishing configuration, the customer complained not receiving summary route with specific loopback address. Which two configurations will fix it? (Choose two.)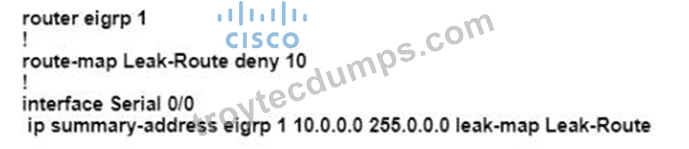
- A. Configure access-list 1 permit 10.1.1.0.0.0.0.3.
- B. Configure route-map Leak-Route permit 20.
- C. Configure access-list 1 permit 10.1.1.1.0.0.0.252.
- D. Configure access-list 1 and match under route-map Leak-Route.
- E. Configure route-map Leak-Route permit 10 and match access-list 1.
Answer: A,E
Explanation:
Explanation
When you configure an EIGRP summary route, all networks that fall within the range of your summary are suppressed and no longer advertised on the interface. Only the summary route is advertised. But if we want to advertise a network that has been suppressed along with the summary route then we can use leak-map feature. The below commands will fix the configuration in this question:
R1(config)#access-list 1 permit 10.1.1.0 0.0.0.3
R1(config)#route-map Leak-Route permit 10 // this command will also remove the "route_map Leak-Route deny 10" command.
R1(config-route-map)#match ip address 1
NEW QUESTION # 379
Refer to the exhibit.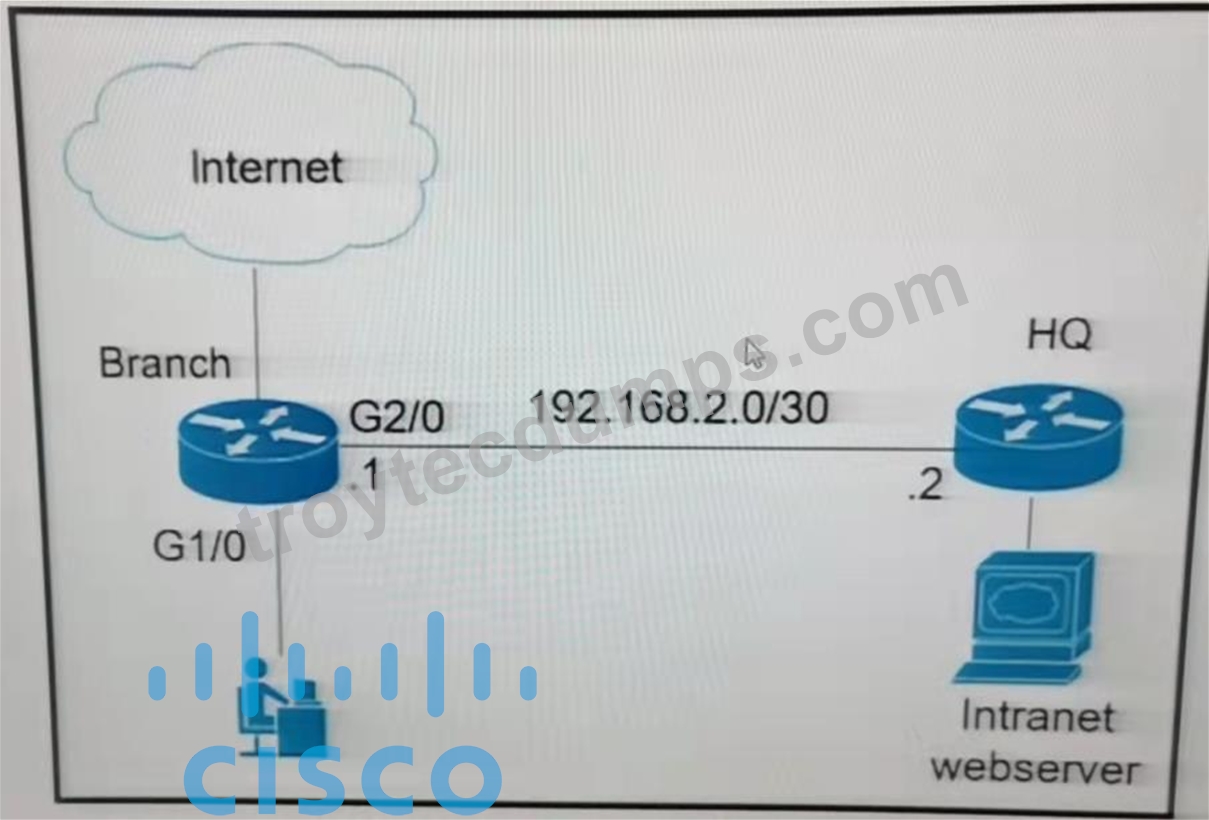
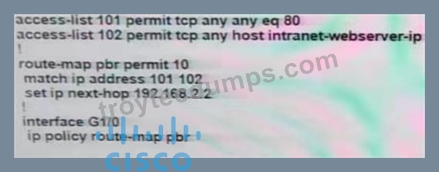
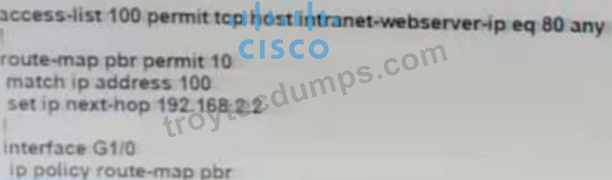
The branch router is configured with a default route toward the internet and has no routes configured for the HQ site that is connected through interface G2/0. The HQ router is fully configured and does not require changes. Which configuration on the branch router makes the intranet website (TCP port 80) available to the branch office users?
- A.
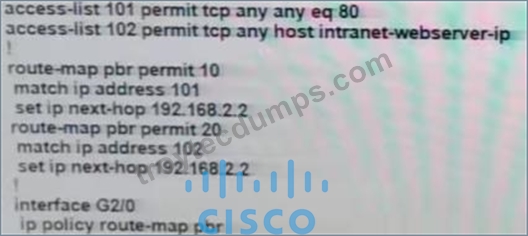
- B.
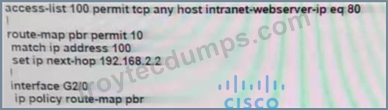
- C.
- D.
Answer: C
Explanation:
the ACL 101 matches all HTTP pakects while the ACL 102 matches TCP packets destined to Intranet webserver. These packets will be sent to HQ router.
If a match command refers to several objects in one command, either of them should match (the logical OR algorithm is applied). For example, in the match ip address 101 102 command, a route is permitted if it is permitted by access list 101 or access list 102.
NEW QUESTION # 380
Refer to the exhibit.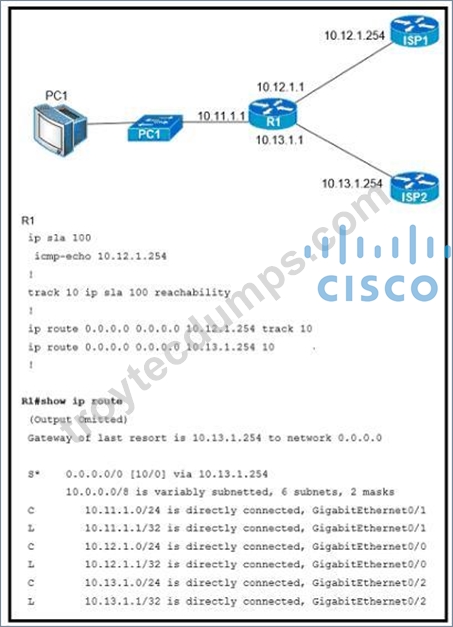
An engineer is monitoring reachability of the configured default routes to ISP1 and ISP2. The default route from ISP1 is preferred if available. How is this issue resolved?
- A. Use the same AD for both default routes
- B. Use the icmp-echo command to track both default routes
- C. Start IP SLA by matching numbers for track and ip sla commands
- D. Start IP SLA by defining frequency and scheduling it
Answer: D
Explanation:
Reference: https://www.cisco.com/c/en/us/support/docs/ip/ip-routing/200785-ISP-Failover-with-default- routes-using-I.html In the above configuration we have not had activated our IP SLA operation. We can start it with this command:
R1(config)#ip sla schedule 100 life forever start-time now
Also we should specific the rate of ICMP echo:
R1(config-ip-sla-echo)#frequency 5 // Send ICMP echo every 5 seconds
NEW QUESTION # 381
Refer to the exhibit. An engineer configures SW101 to send OSPFv3 interfaces state change messages to the server.
However, only some OSPFv3 errors are being recorded.
Which organization resolves the issue?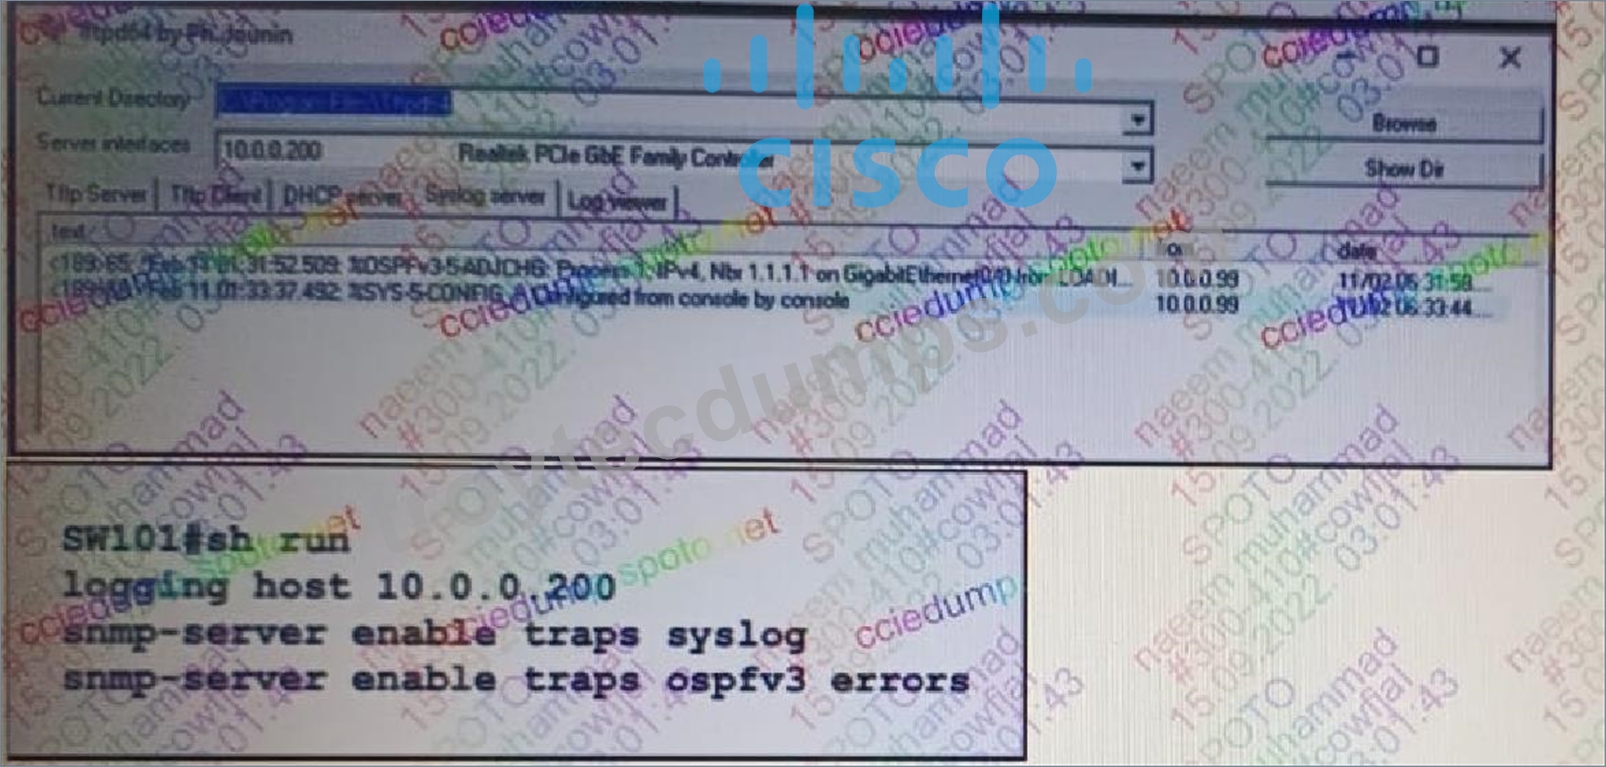
- A. snmp-server enable traps ospfv3 state-change if-state-change
- B. snmp-server-enable traps ospfv3 state-change if-state-change neighbor-state-change
- C. snmp-server-enable traps ospfv3 state-change neighbor-state-change.
- D. snmp-server-enable traps ospfv3 state-change restart-status-change
Answer: B
NEW QUESTION # 382 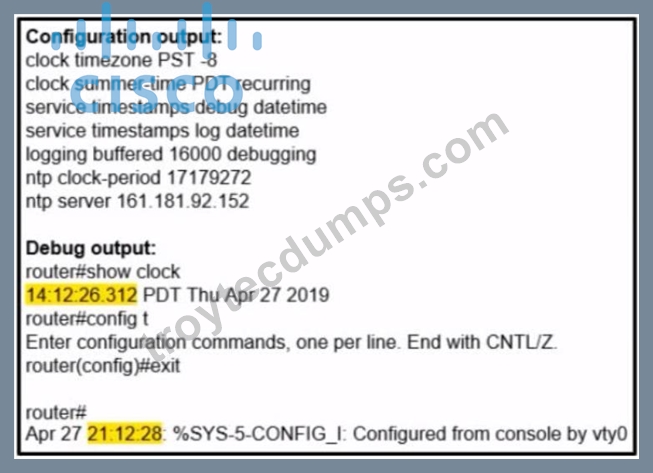
Refer to the exhibit. A network administrator configured NTP on a Cisco router to get synchronized time for system and logs from a unified time source The configuration did not work as desired Which service must be enabled to resolve the issue?
- A. Enter the service timestamps log datetime console global command.
- B. Enter the service timestamps log datetime clock-period global command
- C. Enter the service timestamps log datetime localtime global command.
- D. Enter the service timestamps log datetime synchronize global command.
Answer: C
NEW QUESTION # 383
Refer to the exhibit.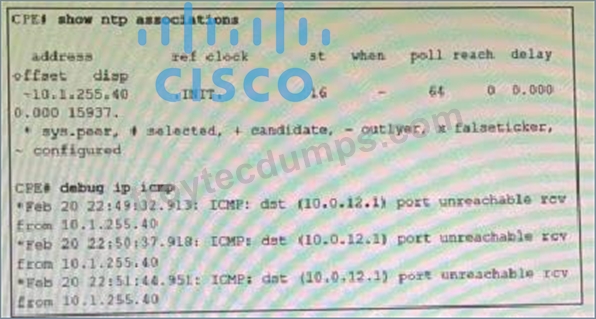
An administrator is troubleshooting a time synchronization problem for the router time to another Cisco IOS XE-based device that has recently undergone hardening. Which action resolves the issue?
- A. Allow NTP in the ingress ACL on 10.1.225.40 by permitting UDP destined to port 123.
- B. NTP service is disabled and must be enabled on 10.1.225.40.
- C. Ensure that he CPE router has a valid route to 10.1.255. 40 for NTP and rectify if not reachable.
- D. Allow NTP in the ingress ACL on 10.1.255.40 by permitting TCP destined to port 123.
Answer: B
NEW QUESTION # 384
Refer to the exhibit. Which option represents the minimal configuration that allows inbound traffic from the 172.16.1.0/24 network to successfully enter router R, while also limiting spoofed
10.0.0.0/8 hosts that could enter router R?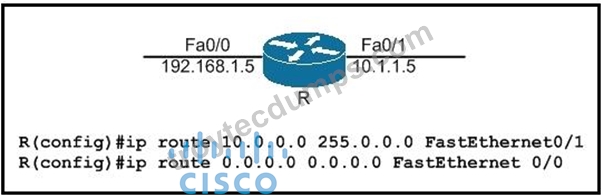
- A. (config)#ip cef
(config)#interface fa0/0
(config-if)#ip verify unicast source reachable-via rx allow-default - B. (config)#ip cef
(config)#interface fa0/0
(config-if)#ip verify unicast source reachable-via rx - C. (config)#no ip cef
(config)#interface fa0/0
(config-if)#ip verify unicast source reachable-via rx - D. (config)#interface fa0/0
(config-if)#ip verify unicast source reachable-via any
Answer: A
NEW QUESTION # 385
The network administrator configured CoPP so that all HTTP and HTTPS traffic from the administrator device located at 172.16 1.99 toward the router CPU is limited to 500 kbps. Any traffic that exceeds this limit must be dropped.
access-list 100 permit ip host 172.16.1.99 any
!
class-map CM-ADMIN
match access-group 100
!
policy-map PM-COPP
class CM-ADMIN
police 500000 conform-action transmit
!
interface E0/0
service-policy input PM-COPP
CoPP failed to capture the desired traffic and the CPU load is getting higher.
Which two configurations resolve the issue? (Choose two.)
- A. no access-list 100access-list 100 permit tcp host 172.16.1.99 any eq 80
- B. interface E0/0no service-policy input PM-COPP!control-planeservice-policy input PM-COPP
- C. no access-list 100access-list 100 permit tcp host 172.16.1.99 any eq 80access-list 100 permit tcp host
172.16.1.99 any eq 443 - D. policy-map PM-COPPclass CM-ADMINno police 500000 conform-action transmitpolice 500 conform-action transmit
- E. policy-map PM-COPPclass CM-ADMINno police 500000 conform-action transmitpolice 500 conform- action transmit!control-planeservice-policy input PM-COPP
Answer: B
NEW QUESTION # 386 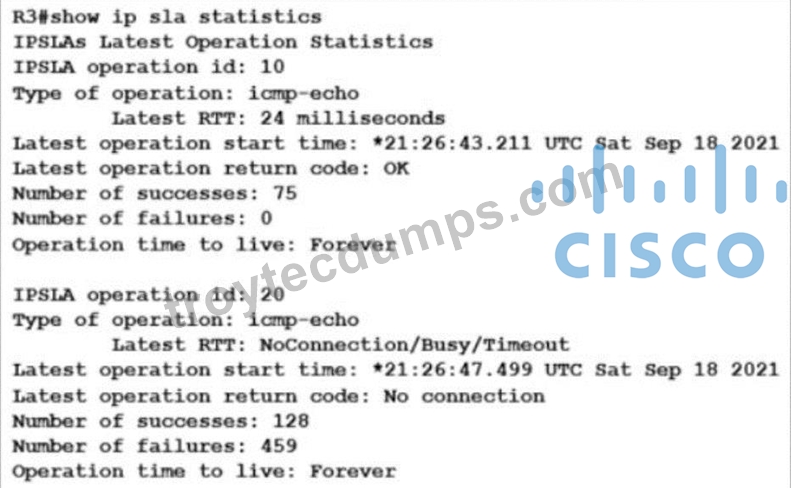
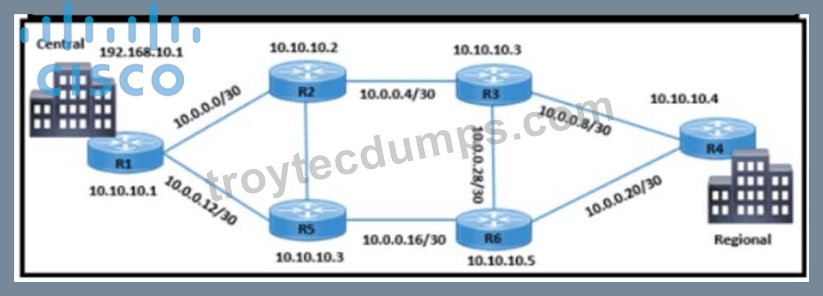
Refer to me exhibit Traffic from R3 to the central site does not use alternate paths when R3 cannot reach 10
10 10 2 Traffic on R3 destined to R4 takes an alternate route via 10 10 10.6 when 10 10 10 4 is not accessible from R3 Which configuration switches traffic destined to 10 10 10 2 from R3 on the alternate path''
- A. R3(config)#ip route 192.168.10.1 255.255.265.255 10.10.10.2 track 20
- B. R6(config)#ip route 10.10.10 3 255.255.255.255 10.0.0.30
- C. R3(config)#track( 20 ip sla 20 reachability
- D. R2(config)#ip route 10.10 10 3 255 255.255 255 10.0.0.6
Answer: A
NEW QUESTION # 387
......
Cisco 300-410 (Implementing Cisco Enterprise Advanced Routing and Services) Exam is a certification exam that tests the knowledge and skills of IT professionals in implementing advanced routing and services in enterprise networks. 300-410 exam is designed for network engineers, network architects, and other IT professionals who work with Cisco routers and switches. 300-410 exam focuses on advanced routing technologies such as OSPF, BGP, and EIGRP, as well as advanced services such as VPN, QoS, and multicast.
Career and Salary Prospects for Certified Specialists
The Cisco 300-410 exam takes you a step closer to obtaining the CCNP Enterprise certification, which is highly reputable in the IT industry. Whether your goal is to find a new job in the computer networking sphere or get a promotion, this certificate will help you move your career to the next level. The positions that you can go for after getting certified include:
- Network Specialist
- IT Team Leader
- Infrastructure Engineer
- Advanced Technician
Passing the Cisco 300-410 exam and obtaining the associated certification can also be extremely beneficial in financial terms. Thus, if you hold the position of a Systems Engineer, you can earn from $59,000 to $126,000 per year. The average annual income of a Network Engineer ranges from $50,000 to $107,000, while the average salary of an IT Team Leader varies from $54,000 to $131,000.
Pass Cisco 300-410 Test Practice Test Questions Exam Dumps: https://www.troytecdumps.com/300-410-troytec-exam-dumps.html
The Best CCNP Enterprise Study Guide for the 300-410 Exam: https://drive.google.com/open?id=1JYUZPVe4qFpvhzk15_ETEtAVZ2bMkR_V